Compliance, on yourendpoint.
Cloud platforms scan your cloud. ComplianceGuard scans the machines your business runs on, collecting, scoring, and signing SOC 2, ISO 27001, HIPAA, and GDPR evidence locally. Nothing leaves your network.
Windows 10/11 · macOS 12+ · Linux (AppImage/deb) · ~1,265 tests passing · Source-available under BSL 1.1
See it in action
Compliance in minutes, not months.
Scheduled endpoint evidence collection, live coverage tracking, and instant PDF evidence reports, all self-hosted and privacy-first.
Your cloud is covered.
Your endpoints are not.
Cloud compliance platforms see your AWS account. They cannot see the password policy, disk encryption, firewall rules, or event logs on the machines your business actually runs on. That evidence lives on the endpoint, and auditors ask for it. ComplianceGuard lives there too.
Controls and obligations scored across SOC 2, ISO 27001, HIPAA, and GDPR in a single collection pass
Bytes of evidence leave your network unless you explicitly choose to sync
From first scan to a per-control readiness score on the machine itself
How it works
From install to evidence pack,
in minutes.
Install
Run the installer for Windows, macOS, or Linux. No admin privileges, no API keys, no agents to deploy.
Scan
ComplianceGuard reads the OS directly: password policy, firewall, disk encryption, audit logging.
Connect AWS
Add credentials once, encrypted locally. Cloud evidence joins the same pack automatically.
Hand off
Export an auditor-ready PDF evidence pack, mapped control-by-control to the framework.
Output shown is illustrative. Actual results depend on your machine configuration.
What it collects
Eight categories.
One scan.
ComplianceGuard reads each source directly from the operating system, with no agent to deploy and no API key. Every item is hashed with SHA-256 and mapped to the controls auditors actually check.
The same collection pass covers the macOS equivalents, and connecting your AWS account once brings IAM, S3 bucket policies, and security groups into the same evidence pack.
Event logs
Security, System, and Application logs
Security settings
Password and audit policies, registry options
Services
Defender, Windows Update, firewall service status
Firewall
Domain, Private, and Public profile configuration
User accounts
Local accounts and admin group membership
Network
Interfaces, open ports, routing tables
Software
Registry-based inventory of installed programs
File permissions
ACLs on critical system paths
The product
Evidence collection,
down to the operating system.
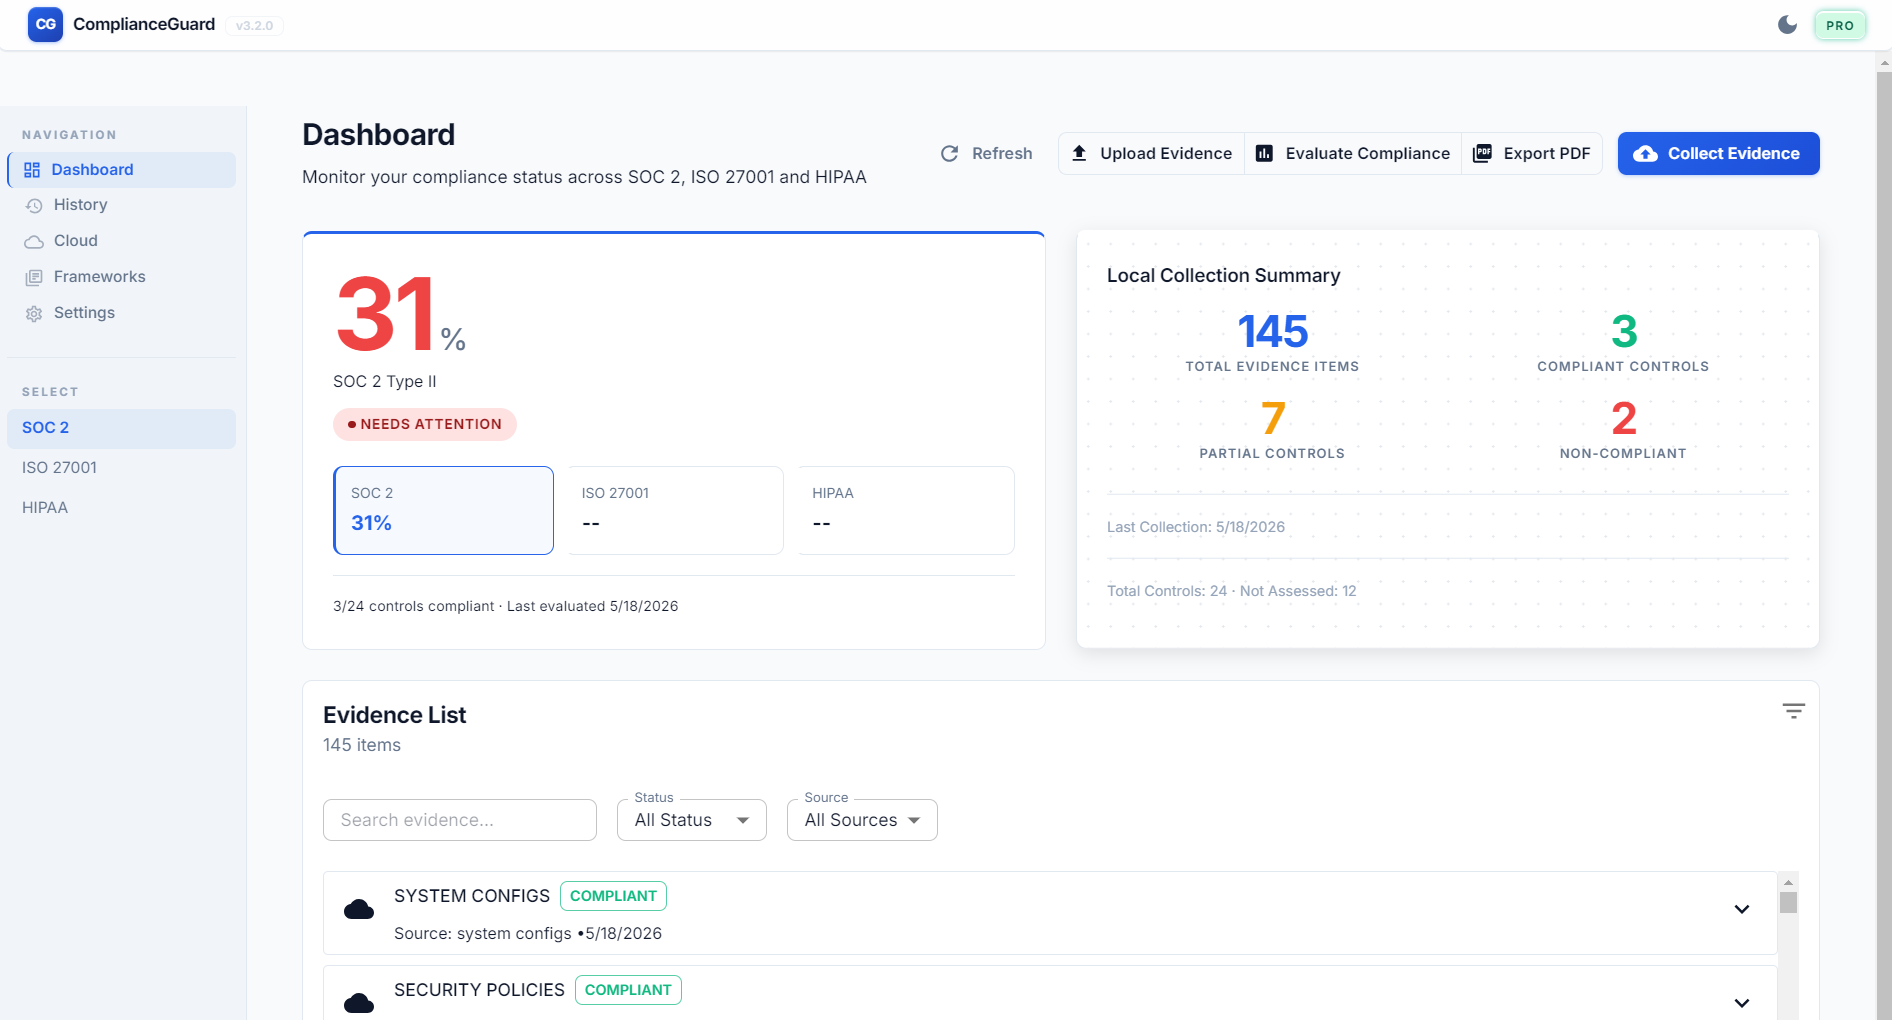
Coverage scoring
Know exactly where you stand.
Your evidence coverage updates the moment a scan completes. See which of the 43 SOC 2 criteria have the evidence they need and which are missing it, with remediation scripts for the gaps, before you ever engage an auditor.
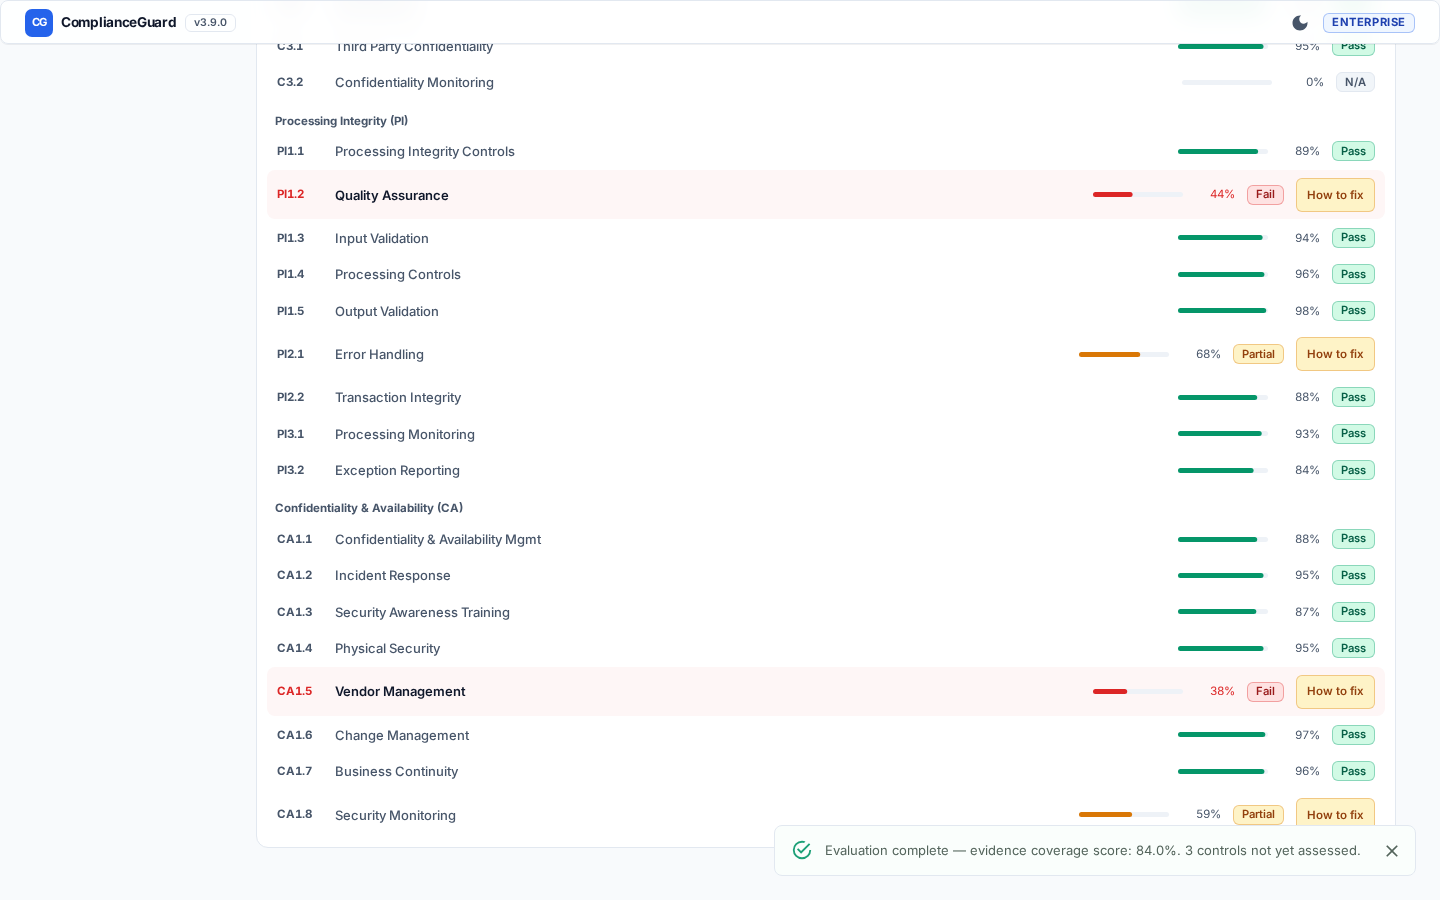
Control heatmap
Every control, color-coded.
Every SOC 2 control at a glance: passing, partial, and failing, with per-control gap details and inline remediation scripts for the findings that can be automated.
More surfaces
Built for the whole compliance journey.
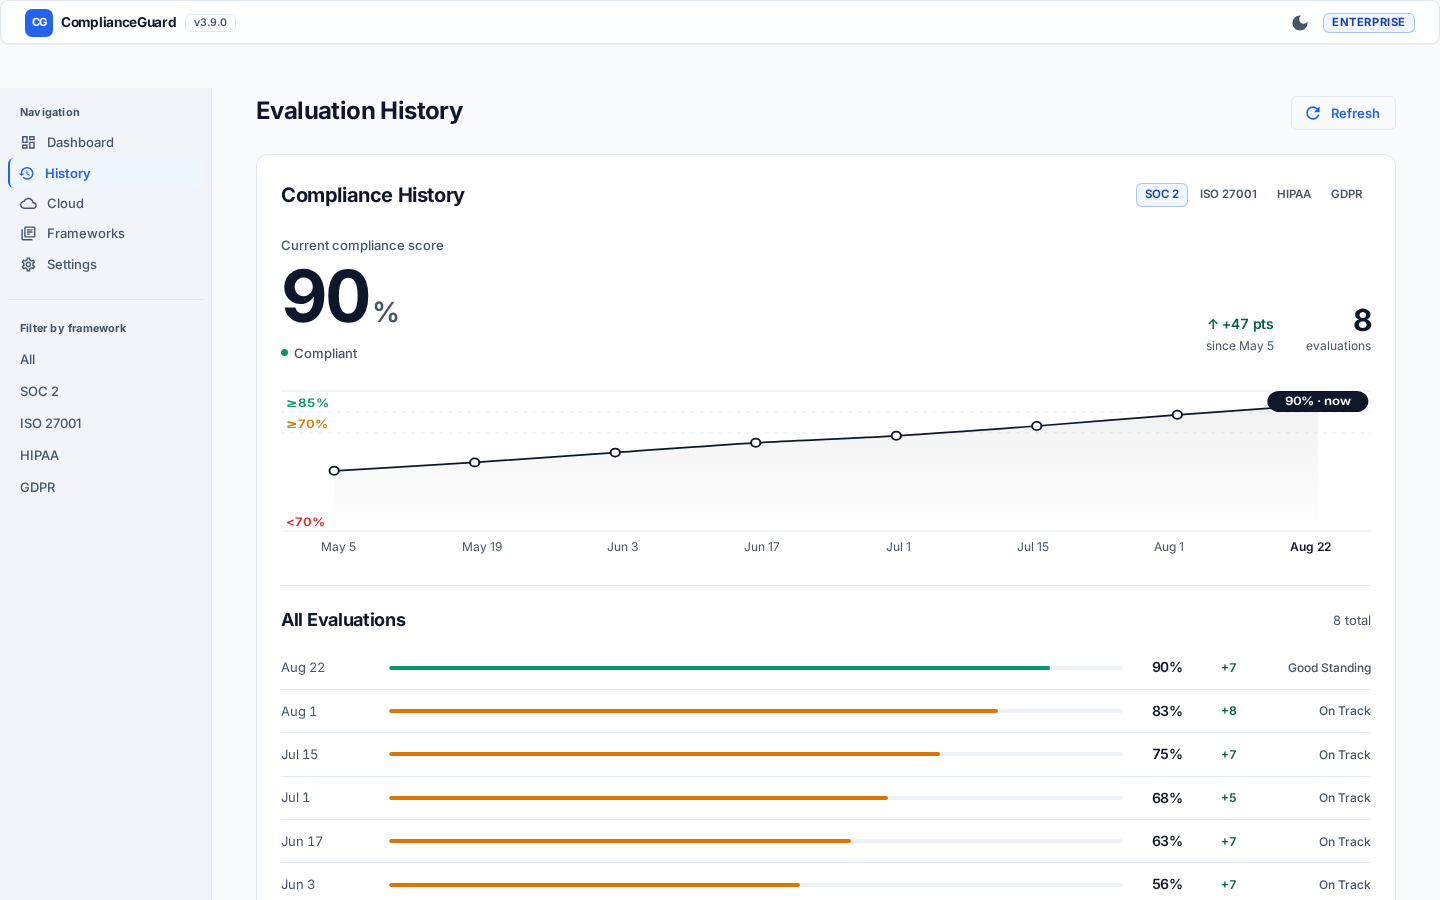
Track readiness over time.
Your score, zone-banded across the timeline, with per-framework tabs so every scan's impact on SOC 2, ISO 27001, HIPAA, and GDPR is visible at a glance.
One connection. Automatic cloud evidence.
Connect your AWS account once. IAM configurations, S3 bucket policies, and security settings join the same evidence pack on every scan.
Hand it to your auditor on day one.
Every evidence pack exports as a PDF mapped control-by-control to the framework. No reformatting. No back-and-forth.
Credentials never leave the machine.
AWS credentials are encrypted at rest with HKDF-SHA256-derived Fernet keys and stored locally. Evidence stays in your local database.
Works without an internet connection.
Evidence collection and reporting run fully offline, built for air-gapped environments and restricted networks.
Frameworks
Four frameworks.
One evidence engine.
The same OS-level evidence collection powers SOC 2, ISO 27001, HIPAA, and GDPR, mapped directly to the controls auditors actually check.
SOC 2
The real 2017 criteria.
43 criteria from the 2017 Trust Services Criteria (33 Common Criteria plus Availability, Confidentiality, and Processing Integrity supplements), scored by evidence coverage. The standard for enterprise SaaS deals.
ISO 27001
Annex A, 2022 edition.
All 93 controls of the ISO/IEC 27001:2022 Annex A across Organizational, People, Physical, and Technological categories. Required for European enterprise contracts.
HIPAA
Security Rule, in one pass.
47 safeguards across all five 45 CFR Part 164 sections, required and addressable. Built for health-tech.
GDPR
Readiness, stated honestly.
38 obligations from EU 2016/679 classified by what endpoint evidence can actually establish, so organizational duties are never scored as done because a scan ran.
Architecture
Nothing leaves your network.
Ever.
Every byte of evidence stays inside the boundary you control. We don’t have a database for your data, because we never see it.
0
bytes uploaded to our servers
100%
of evidence stays on your machine
AES-256
credential encryption at rest
AICPA TSC-mapped
Every criterion mapped to the Trust Services Criteria, in the structure auditors expect for SOC 2 readiness.
Offline-verified licensing
Ed25519 public-key license verification with no license server and no phone-home, which fits the air-gap story.
Source-available, BSL 1.1
You can read the code that reads your system. Every line of evidence collection and scoring logic is auditable.
How we compare
Different by architecture.
Cloud-first platforms automate evidence through SaaS, cloud, identity, and MDM integrations. ComplianceGuard collects it directly from the machines themselves. The difference is where the evidence comes from, and where it stays.
| Capability | ComplianceGuard | Vanta | Drata |
|---|---|---|---|
| Evidence source | The endpoint itself | Cloud + SaaS/identity/MDM integrations | Cloud + SaaS/identity/MDM integrations |
| Data stays on your machine | |||
| Works offline / air-gapped | |||
| Compliance frameworks | SOC 2 · ISO 27001 · HIPAA · GDPR | Broad multi-framework coverage | Broad multi-framework coverage |
| Pricing | Flat rate · free tier | Annual platform fee | Annual platform fee |
| Setup time | Minutes | Days to weeks | Days to weeks |
| Source code | BSL 1.1 source-available | Proprietary | Proprietary |
| Free tier |
Competitor capabilities based on publicly available information as of 2026.
Built for the rooms
internet doesn’t reach.
Government, defence and regulated finance teams need evidence that proves itself without phoning home. Ships fully offline with a cryptographic audit trail.
Contact salesTamper-evident audit log
Every evaluation, evidence collection and config change is appended to a SHA-256 hash chain. One altered byte breaks the chain, verifiable end-to-end in one request.
RBAC: admin + auditor
Separate read-only auditor accounts. Last-admin lockout guard. First registered user seeded as admin via migration.
NDJSON streaming export
Stream every evidence item, evaluation and audit row as newline-delimited JSON, scoped to the authenticated tenant.
Hardened, air-gapped deploy
Pre-bundled Docker images. Hardened Nginx (TLS 1.2+, HSTS, no server banner). ENTERPRISE_MODE disables telemetry. Zero outbound calls.
An honest fit
Some teams shouldn’t use us.
Sending you to a better tool costs us a download and saves you a quarter. If any of these is your situation, the alternatives below are genuinely stronger for you.
Cloud-only audits
not usYour SOC 2 story is your AWS or GCP configuration, and nothing that runs on the machines your team actually uses.
Better fit: Vanta or Drata cover cloud infrastructure evidence far better. Vanta · Drata.
You can't install software on the endpoints being audited
not usEvidence collection runs on the machines themselves, so the desktop app has to be installed there. Managed hosting removes the server work; it does not remove the endpoint app.
Better fit: Cloud-first platforms that collect through your MDM or identity provider may fit better.
A one-login GRC suite
not usYou want policies, risk registers, training tracking, vendor intake, and evidence bundled into one hosted product with SSO.
Better fit: A dedicated GRC platform is the right shape for that. ComplianceGuard is an evidence engine, and we would rather you bought the tool that covers the whole program.
- You run Windows, macOS, or Linux endpoints, Intel or Apple Silicon
- Your next audit is SOC 2, ISO 27001, HIPAA, or GDPR readiness
- You want evidence collected from the machine, not only cloud APIs
- You need it to work offline, air-gapped, or fully self-hosted
If that reads like your team, the free tier scores all 43 SOC 2 criteria on your first machine before you pay anything.
See plans and pricingOr download the app firstPricing
Start free. Scale when ready.
Free
See exactly where you stand on SOC 2 before you pay anything.
- Evidence collection (all 8 categories, all 3 OSes)
- All 43 SOC 2 criteria, overall coverage score
- Evidence coverage and readiness trend
- 1 machine · 1 user · community support
Pro
Everything you need to walk into the audit with a complete evidence pack.
- SOC 2 (43 criteria) · ISO 27001:2022 (93) · HIPAA (47) · GDPR (38)
- Per-control scoring, gaps, and remediation scripts
- Control heatmap and evidence coverage trend per framework
- Manual evidence upload + evaluation history
Enterprise
Tamper-evident, air-gapped sovereignty for regulated industries.
- Everything in Pro
- Tamper-evident audit log (HMAC-SHA256 hash chain)
- RBAC (admin and auditor roles)
- Custom PDF branding
Self-hosted pricing, billed annually. Managed hosting available.
Compare all plans and managed hostingFAQ
Common questions.
Four, from a single collection pass: SOC 2 (43 criteria from the 2017 Trust Services Criteria), ISO/IEC 27001:2022 (all 93 Annex A controls), the HIPAA Security Rule (47 safeguards), and GDPR (38 obligations). The same OS-level evidence feeds all four, each scored by evidence coverage rather than a checkbox claim of compliance.
Every evidence pack is mapped criterion-by-criterion to the AICPA Trust Services Criteria, the exact framework SOC 2 auditors work from. The PDF export is organized the way auditors expect, so there's no reformatting and no back-and-forth. A formal SOC 2 report still requires a licensed CPA firm; ComplianceGuard gets you to that engagement prepared.
They collect through their cloud integrations; ComplianceGuard collects on the machines themselves. Password policies, firewall rules, disk encryption, and event logs. That evidence lives on the endpoint, not in AWS. Many teams run both: a cloud platform for SaaS integrations, ComplianceGuard for the endpoint evidence those platforms structurally can't see.
Don't trust claims; read the code. ComplianceGuard is source-available under BSL 1.1, so every line that touches your machine is auditable. Licensing uses offline Ed25519 public-key verification, credentials are encrypted with HKDF-derived Fernet keys, and ~1,265 tests run on every commit. Most importantly, the architecture means we never receive your evidence. It stays on your disk, under your control.
You can, and most first SOC 2 audits start that way. ComplianceGuard automates the collection: instead of checking firewall settings by hand, running scripts, and copying output into a spreadsheet, it reads everything in about 30 seconds and formats it the way your auditor expects.
It stays on your machine. ComplianceGuard reads from your OS and your AWS account, writes to a local SQLite database, and exports a PDF when you ask. There is no upload step and no telemetry. Evidence only moves if you explicitly enable the optional multi-machine dashboard sync.
Credentials are encrypted at rest using a Fernet key derived via HKDF-SHA256 from your local secret key. They are decrypted in memory only at evidence-collection time and are never transmitted anywhere. The source code is available, so you can verify this yourself.
No auditor marketplace. Use whichever firm you want. No 40-app integration catalog, either; the focus is evidence, not workflow chrome. And no lock-in: evidence is stored locally in standard formats, so you can export it and switch tools at any time.
Your next enterprise deal
is waiting on a SOC 2 report.
Walk into the audit with evidence collected from the machines themselves: scored, signed, and under your control.
No account required. No cloud storage. No credit card for the free tier.